
A security researcher from Hyderabad co-founded an AI startup that just exposed critical vulnerabilities in OpenAI systems, earning a modest bug bounty but proving a larger point about how artificial intelligence reshapes offensive security research.
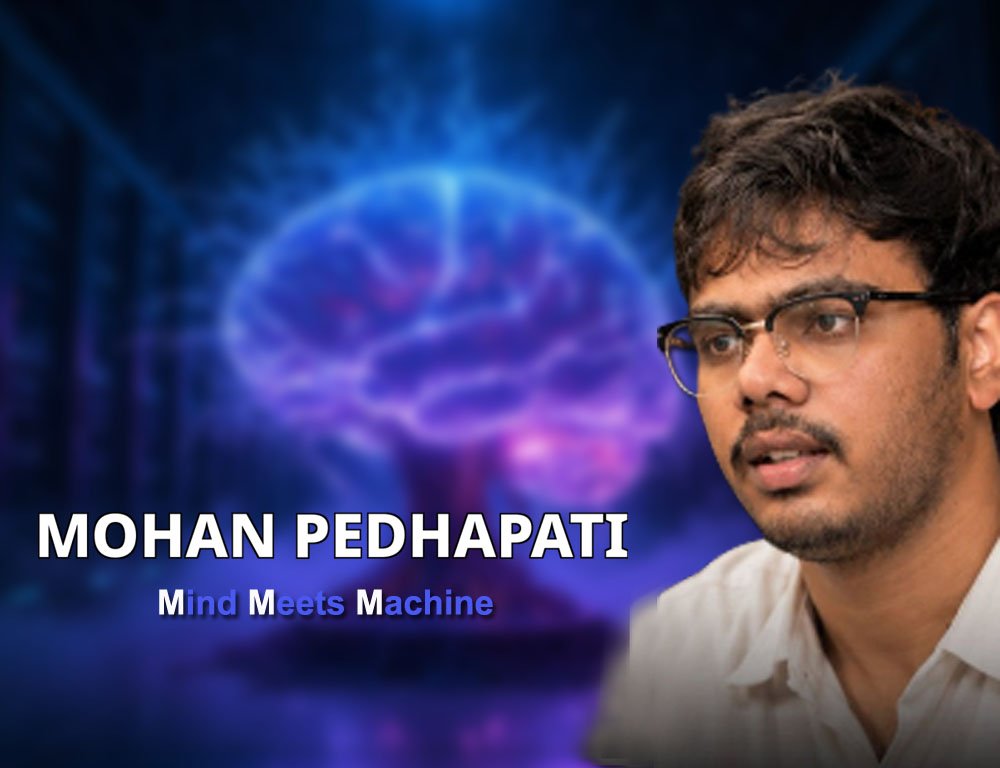
The stakes keep rising as AI models embed themselves into critical infrastructure. Malicious exploitation of such flaws could trigger serious national security consequences, according to Mohan Pedhapati, the researcher behind the discovery.
Pedhapati first gained recognition when his work on prototype pollution, a browser security vulnerability, landed fourth on PortSwigger’s 2021 ranking of top web hacking techniques. That research eventually led him to found Electrovolt Infosec, a cybersecurity firm that partnered with German security company Cure53 and pulled in roughly €1.5 million in revenue from clients across India and abroad.
Cure53 later hired him as a consultant without any formal interview. His published research plus a recommendation from another researcher sealed the deal.
In August 2025, Pedhapati teamed up with Harsh Jaiswal, an Indian researcher known for Apple vulnerability discoveries, and Zayne Zhang, a Cambridge dropout, to launch Hacktron AI. The startup uses artificial intelligence to automate vulnerability scanning and continuously test software as developers ship changes.
Hacktron secured a spot in Project Europe, an accelerator backed by European founders that invested €200,000. By May 2026, the company announced a $2.9 million pre-seed round and reported $240,000 in revenue during its first nine months, with clients including Perplexity AI and Supabase.
The OpenAI research began not with ChatGPT itself but with OpenAI’s public support forum. That forum runs on widely deployed software and lets users log in with OpenAI credentials. The team, including Pedhapati, Jaiswal, and Rahul Maini, found a flaw in an image-processing component that handles iPhone photo uploads. A maliciously crafted image could give an attacker control of the forum server.
A second weakness in OpenAI’s authentication system compounded the problem. Together, the flaws could potentially expose ChatGPT and Codex accounts belonging to users who had logged into the forum, including OpenAI employees with access to internal source code repositories.
The team spent about three months on the broader research. They identified the critical vulnerability in July 2026 and reported it through responsible disclosure channels. OpenAI fixed the issues and paid $6,500 for the work.
Pedhapati sees the episode as evidence that AI compresses timelines for security research. Work that once required months and large teams can now happen with just a handful of people. He holds an O-1 visa, reserved for people with extraordinary ability, and plans to move to the US permanently next year.