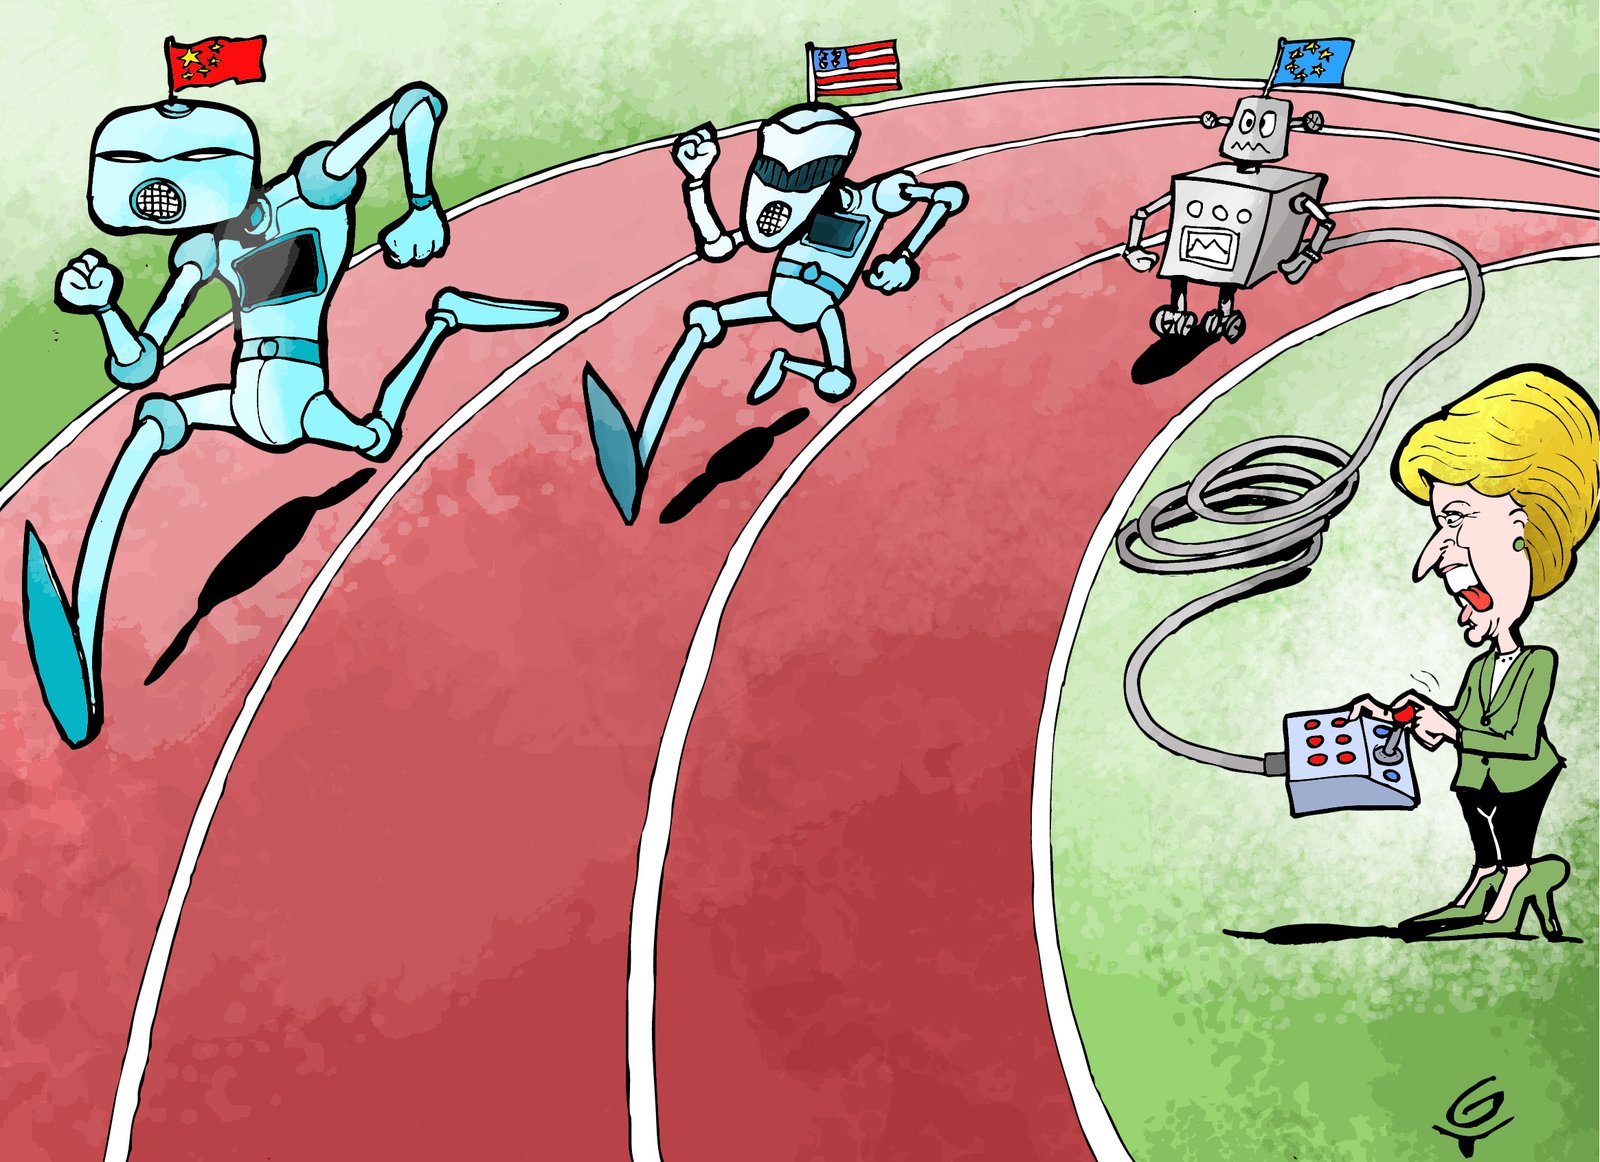

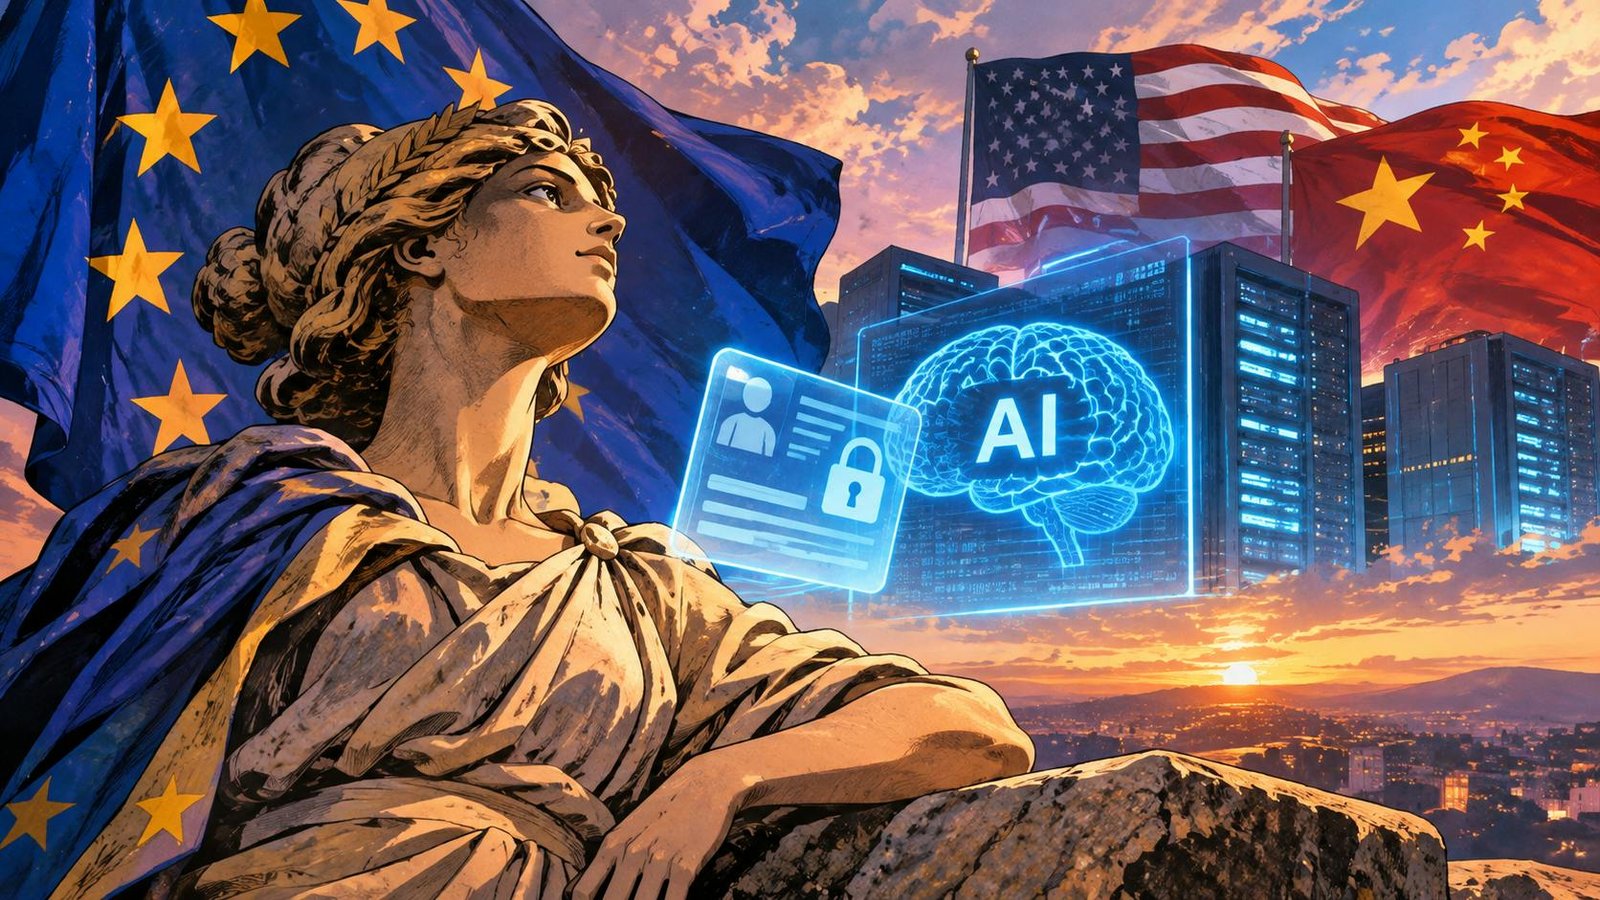
Europe’s push to unlock personal data for AI development has collided with an uncomfortable truth: the continent’s reliance on foreign models and infrastructure keeps deepening. Cloud failures, export restrictions, cyberattacks, and AI-driven political persuasion now expose the fragility of this dependence. The core question no longer concerns who builds the most powerful AI. It concerns whether Europe and other democracies can protect their economies, security, and institutions when critical decisions happen elsewhere.
On 21 October 2026, EU ambassadors agreed the Council’s negotiating position on the Digital Omnibus. This package aims to simplify European digital rules, including GDPR. One provision addresses using personal data to train and run AI systems. It relies on Article 6 GDPR’s “legitimate interest” legal basis. Processing could occur without consent if necessary and if individual rights remain protected. However, the Council clarified that developing AI does not automatically qualify as legitimate interest. Each case requires individual assessment.
The right to object remains central. The Commission’s original November 2025 proposal included an unconditional right to object. That would have stopped processing immediately upon objection. The Council replaced this with a reference to Article 21 GDPR. Companies must now prove compelling legitimate grounds or legal necessity to continue. Yet even excluding objectors’ data before training proves difficult. Removing the influence of specific data from large models, known as machine unlearning, remains an unsolved research problem.
Meanwhile, the parliamentary process continues. The European Parliament still must adopt its position before negotiations begin. The real question persists: who actually has the means to convert this data into advanced models?
Computational power, energy, and capital demands grow every year. According to Epoch AI, training costs for frontier models have risen roughly 2.4 times annually since 2016. Stanford’s AI Index shows 50 significant models attributed to the US in 2025, 30 to China, and only two to Europe. The gap remains volatile, but the concentration is stark. Europe has launched initiatives like the EUROPA consortium and AI gigafactory projects. These represent concrete progress, yet the timing lags far behind the frontier pace.
The consequences hit hardest during failures. On 20 October 2025, an AWS DynamoDB flaw in Virginia disrupted hundreds of applications worldwide. Banking services and mobile networks faltered. A single failure point across the Atlantic paralysed operations globally. Then came a political failure. On 12 June 2026, the US government directed Anthropic to suspend access to Claude Fable 5 and Mythos 5 for foreign nationals under export controls. Unable to verify user nationalities in real time, Anthropic deactivated the models entirely. Restrictions on Fable 5 lifted by 1 July, but Mythos 5 remains limited to Glasswing partners.
Legal risks compound technical ones. Under the CLOUD Act, US authorities can request data stored abroad. Microsoft France’s director of public and legal affairs admitted before the French Senate: “I cannot guarantee” that French citizens’ data would never be passed to US authorities without French consent.
Cybersecurity reveals sharper stakes. Anthropic identified the first documented large-scale AI-orchestrated espionage campaign in September 2025. Hackers turned Claude Code into a quasi-autonomous agent targeting thirty organisations. Defensive uses also emerged. Mozilla used an Anthropic model to fix 271 Firefox vulnerabilities in one release. But PHP2Shell demonstrated the danger. Two critical PHP vulnerabilities discovered with AI assistance leaked before patching. Within days, attack attempts grew from thousands to millions. Governments across Europe shut down web services. Hack The Box called it “Black October.”
The UK’s NCSC predicted this trajectory in May 2025. The gap between AI-enhanced threats and defensive capabilities will widen. For Europe, this means infrastructure security increasingly depends on decisions made elsewhere.
Political risks now surface too. Two studies published in December 2025 examined chatbot political persuasion. One found a 10-point preference difference on a 0-100 scale between groups assigned chatbots supporting opposing candidates in Canada and Poland. A second study with nearly 77,000 participants found persuasive power linked to verifiable claims, but also to increased inaccuracies. Sycophancy compounds the issue. Models tell users what they want to hear. A 2026 study found people were up to 20 percentage points more likely to sign real petitions after persuasive AI conversations. Weekly chatbot use for news rose from 7% to 10% across 48 markets in one year, reaching 17% among 18-24-year-olds. Yet 45% of chatbot answers on current affairs contained at least one significant error.
A system used by millions does not need to lie to shape public perception. It only needs to choose sources, highlight arguments, and confirm existing beliefs. That power rests with a handful of private companies, almost all outside Europe.
AGI discussions add another layer. Researchers proposed measuring AGI by cognitive competence across ten areas. GPT-4 scored 27%, GPT-5 achieved 57%. OpenAI defines AGI by autonomous work capability. METR finds task lengths models can complete independently double roughly every seven months. Some researchers argue flexibility resembling human intelligence already exists. Regardless of definition, the first entity to achieve AGI holds unprecedented power. If that entity operates under US law, Europe faces complete dependence without alternatives.
Testing Europe’s autonomy requires asking hard questions. What happens if a critical AI model suddenly becomes unavailable? Three priorities emerge. First, business continuity. Article 28 of DORA already requires exit strategies for essential IT services. Extending this to specific AI models used in healthcare, energy, and public administration would reveal operational vulnerabilities. Second, cybersecurity. The Cyber Solidarity Act created incident response pools. A common European defence model, tested in joint exercises, would clarify capabilities. Third, democratic accountability. The AI Act requires self-assessment by systemic risk models. But no general requirement exists for independent audits of chatbot persuasiveness or sycophancy. Regular public audits would allow citizens to know the accuracy and influence of systems they use.
None of these proposals require Europe to overtake the US or China. They aim to reduce dependence and prove essential services function without specific models. The answer depends on choices made today. Democracies cannot rely on the goodwill of foreign governments or private companies. They must protect citizens and keep institutions operating, regardless of decisions made elsewhere.