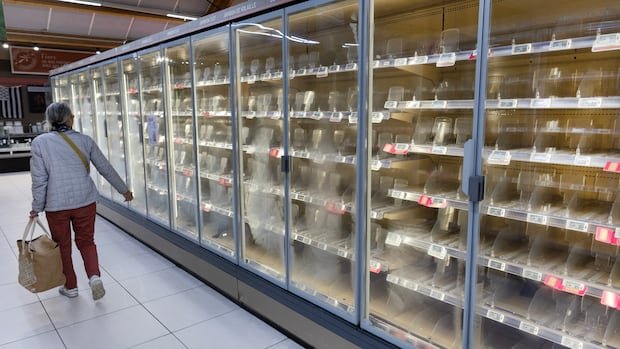

A cyberattack that remotely seized control of supermarket refrigeration units across multiple European locations last week has exposed a chilling vulnerability in the food supply chain. The breach hit SuperValu stores and several UK meat processors, proving that hackers can now weaponize the cold chain itself.
For decades, refrigeration failures meant mechanical breakdowns, power outages, or simple wear and tear. Large facilities countered these risks with routine manual inspections. Smaller retail operations, locked up for 12 hours or more overnight, often skipped such checks entirely.
This incident marks something entirely different. External attackers breached computerized control systems with deliberate intent to disrupt operations and destroy stock. Damage remained limited this time, but the episode serves as a blunt warning about our growing dependence on remote management systems, still before artificial intelligence reaches maturity.
The vulnerability extends far beyond grocery stores. Modern tractors, harvesters, and other farm equipment run on software. A breakdown now stems as often from a computer fault as from diesel or mechanical failure. Service engineers carry laptops alongside socket sets.
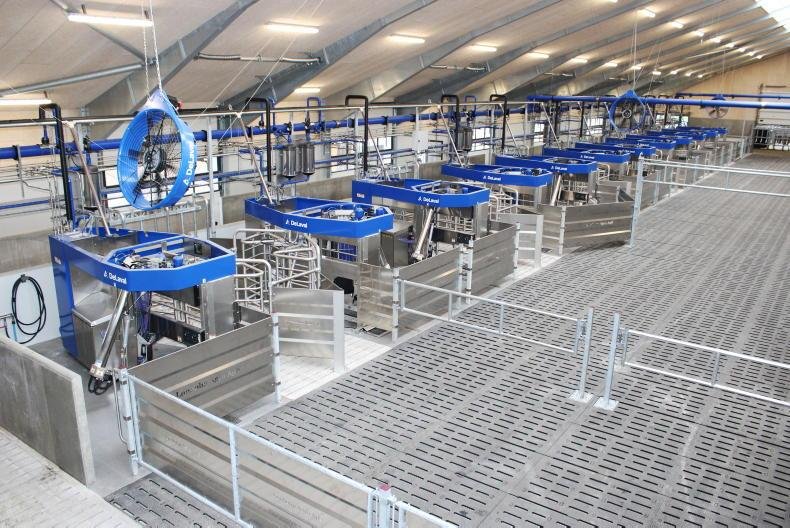
Farming has already entered its third technological age. The first relied on manual labor and horsepower. The second brought mechanization. This emerging era runs on GPS-guided precision planting, robotic milking systems, and AI-monitored calving sheds. Dairy processors operate with strikingly few workers on the factory floor, a stark contrast to the days when 10-gallon churns arrived by flatbed lorry.
Yet food security, a term farm leaders argue gets taken for granted in EU policy debates, now faces a new external and sinister threat. The SuperValu hack demonstrates that as technology adoption accelerates, so does risk.
There exists no path back to creamery cans or horse-drawn ploughs. What the agri-food sector needs instead is preparation for threats that until last week seemed unimaginable.